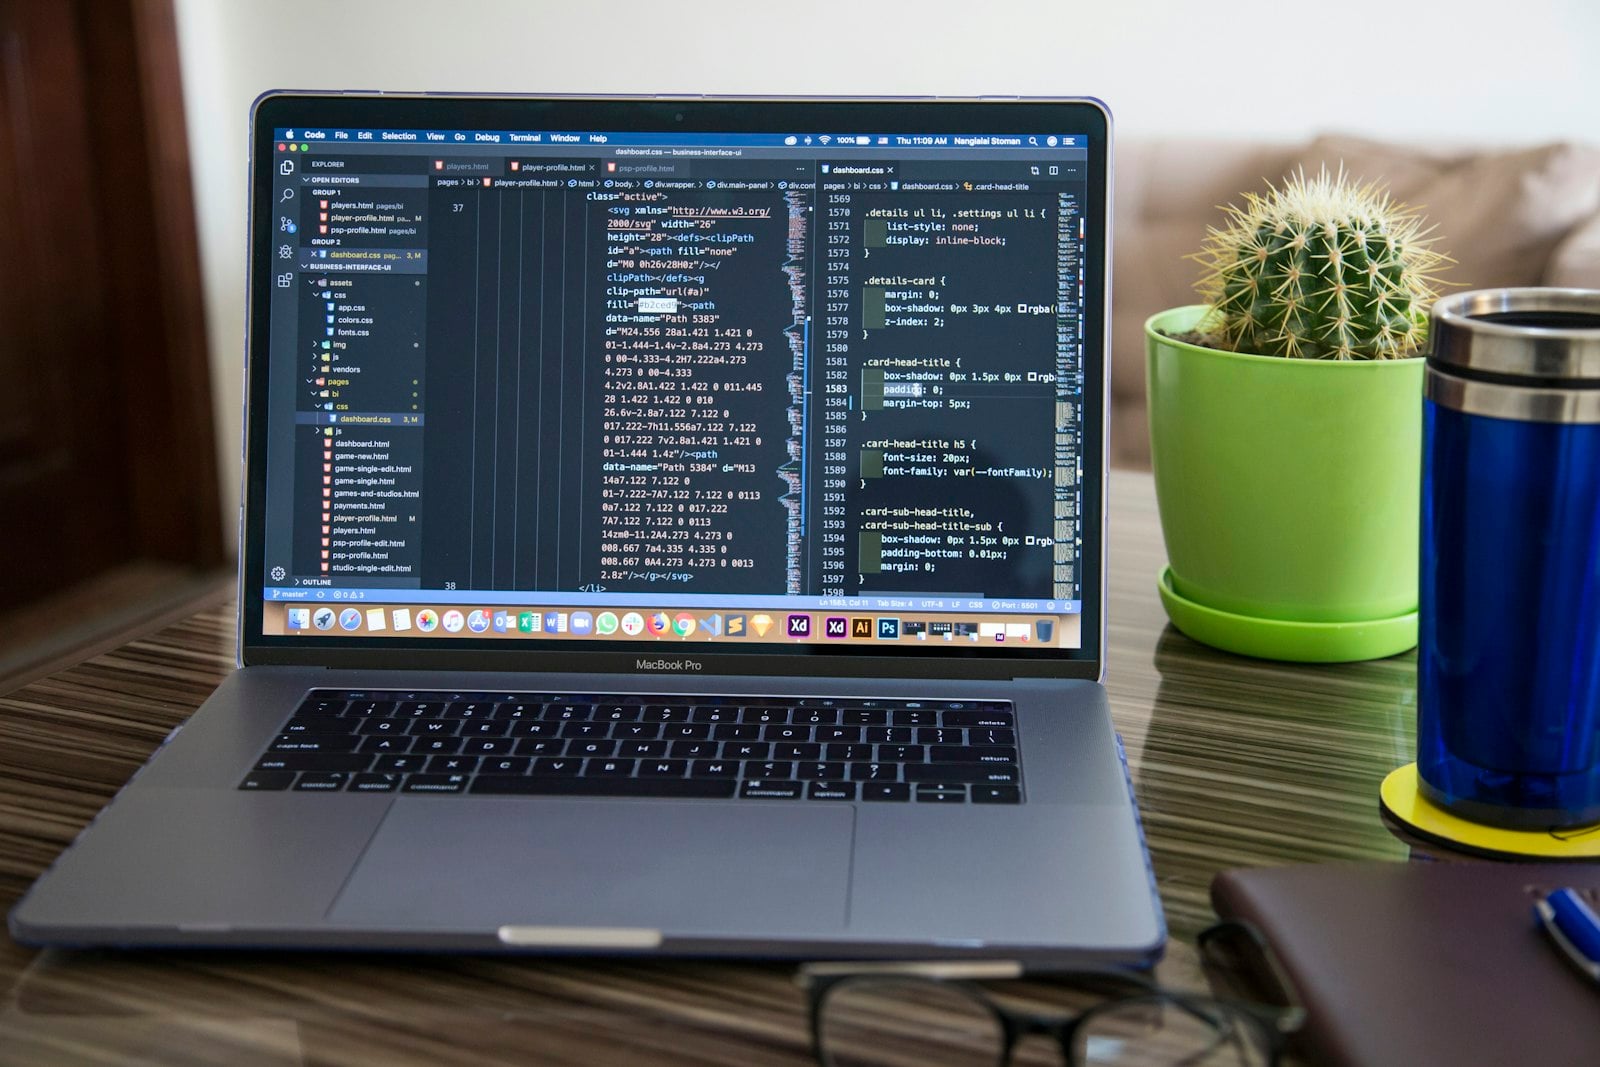
Applying the RBAC permission model to protect 🔐 your Azure Key Vault objects should be used in favor of the access policy option.
The vault access policy is applied at the Key Vault scope. Meaning if you had a dozen secrets in your vault, then you're essentially allowing everyone privileges in the policy access to all of those secrets. A workaround to this is to create a separate key vault for each key vault object, applying a policy on each vault. This creates config and permissions management overhead 😣
Alternatively, if you use the RBAC model, then there's no need for a policy. The majority of RBAC roles are applied at either the control or management planes in Azure. However, there are several data plane built-in roles available for the key vault such as the "Key Vault Crypto User" which allows the 'list' of keys 🔑 or the "Key Vault Secrets User" allowing you to 'get' and 'list' secrets. These RBAC controls can be applied at the entire vault scope or on a per-vault object basis thus securing access to each of your keys/secrets/certificates within the vault. This allows for much more granular permissions, decreases config overhead and provides a higher level of protection for your ☁️ assets.
Do you agree? What authorization method works best for you? I'd love to hear your opinion about this. Let me know in the comments!
About the author
- Hi there! I'm a Cloud Engineer & SRE, documenting my transition into AI/ML Platform Engineering. I write technical deep-dives, hands-on implementation guides, CLI helper scripts, and visual architectures covering cloud, infrastructure, orchestration, governance, and modern AI runtimes.
Comments
Join the discussionThanks for this - never really thought about the difference between the methods. Just sort of "winged" it.
Granularity is (almost always) a good thing! RBAC it is!
Thank you Jake, glad you liked it! And I absolutely agree with you - RBAC all day every day :)
Cloud Architectures
Focuses on high-level system design, provider translations, and architectural reference patterns across multi-cloud ecosystems. Covers service mappings between major cloud providers (AWS to Azure), and structural design choices between managed cloud platforms and self-hosted AI compute infrastructure.